Application roles (EAC)
Application roles give users permissions and capabilities within a particular application. Application roles are assigned to access groups.
Note
This feature is supported for on-premises customers and customers who are not using role-based access control.
Use these application roles to grant permissions and capabilities within an application:
View | The application View role (Application Viewer) has basic access to the Contrast web interface to see scores, libraries, vulnerabilities and comments, but cannot perform edits to traces to the application. 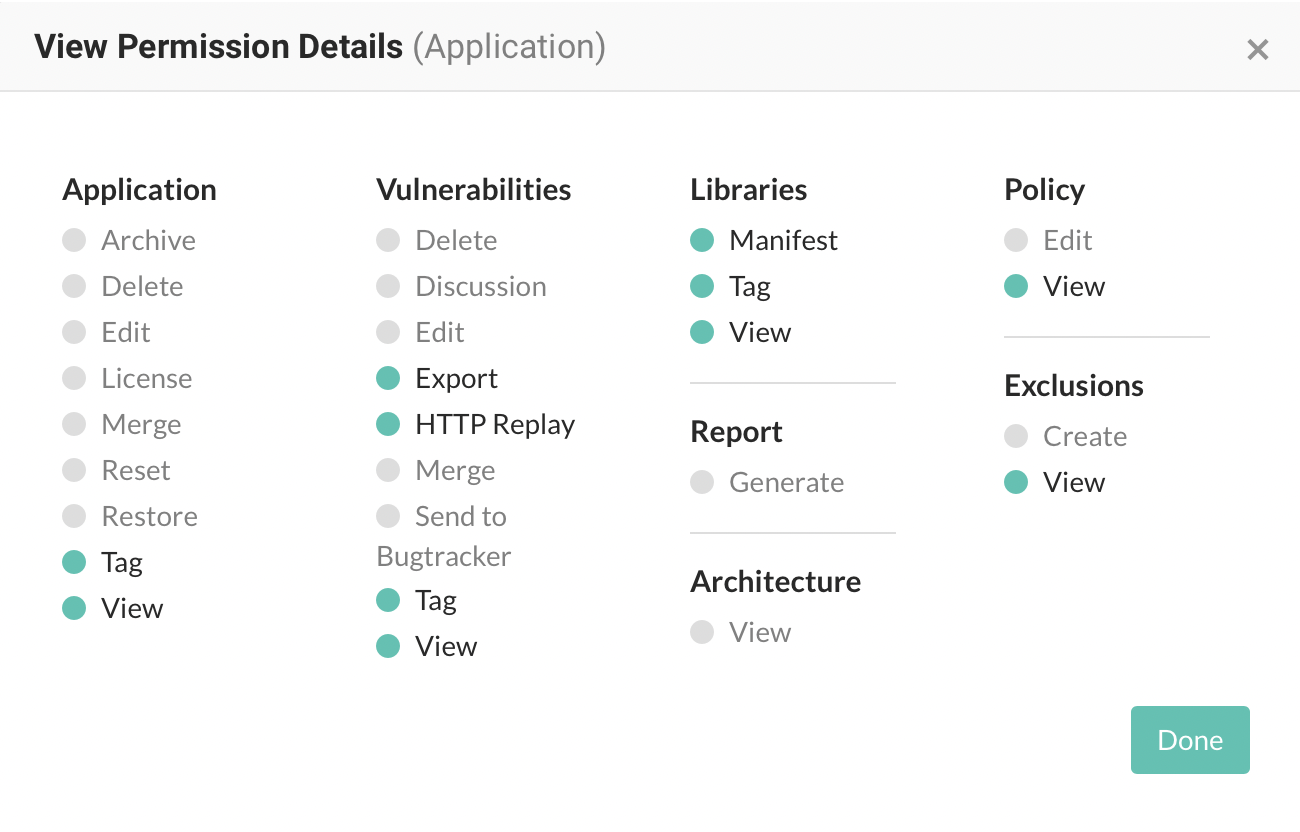 |
Edit | The application Edit role (Application Editor) can remediate findings, add tags, manage vulnerabilities, edit attributes, add or delete applications, and create servers. The majority of Contrast users have this role. |
Rules Admin | The application Rules Admin role (Application Rules Admin) can edit rules and policies in the application, enable Protect, and manage notifications and scoring for the application. |
Admin | The application Admin role (Application Administrator) has no restrictions and can manage other users' access to the application. |
The No Access role blocks user access to the application.
You can add application roles when you create or edit an organization access group.